In the ever-changing landscape of the digital world, cyber security threats pose a constant challenge to businesses and individuals alike. As our reliance on online services and digital connectivity grows, new methods of attack are constantly emerging, putting security systems to the test. Distributed Denial of Service (DDoS) attacks, in particular, have evolved significantly in recent years, highlighting the need to continually adapt our defence strategies.
From massive DDoS attacks to more subtle tactics
DDoS attacks have long been a favourite method used by cybercriminals to cripple websites and online services. Originally, these attacks were characterised by their sheer scale - huge volumes of spoofed traffic were directed at DNS servers to restrict their availability and make services inaccessible to legitimate users. Whilst these massive attacks were effective, they were also relatively easy to detect and defend against, as they generated significant traffic spikes that could be identified by security systems.
More recently, however, cybercriminals have refined their strategies. Instead of relying solely on volume, attackers now distribute smaller amounts of data across various targets and services. This technique aims to circumvent DDoS detection by keeping the attack under the radar. By spreading the attack traffic across multiple vectors, it becomes more difficult for security systems to detect abnormally high levels of traffic and respond accordingly.
The constant evolution of attack patterns
The evolution of DDoS attacks highlights a broader pattern in the world of cyber security: attackers are constantly seeking new ways to circumvent security measures. This cat-and-mouse game between cybercriminals and security experts requires constant adaptation and innovation in defence strategies. It is no longer enough to rely on traditional security measures; organisations must be proactive and focus on detecting more subtle attack patterns.
How a DDoS attack works
A Distributed Denial of Service (DDoS) attack is a malicious attempt to flood a website, server or network with so much traffic that the service becomes overloaded, denying access to legitimate users. Essentially, a DDoS attack aims to fully exhaust the target’s resources in order to disrupt or completely halt its operation.
Step 1: The botnet
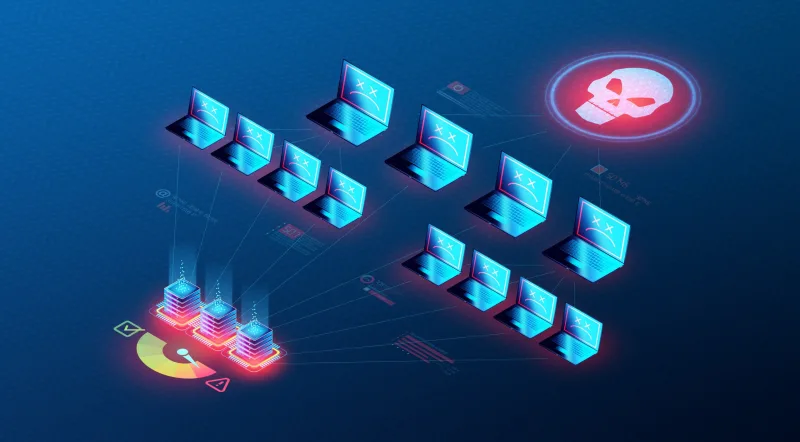
The first step in a DDoS attack often involves setting up a network of compromised computers, known as a botnet. Cybercriminals infect numerous devices with malware so that they can control them remotely. These infected devices, also known as bots, can be spread across the internet and serve as launch points for the attack. The botnet enables the attacker to scale the attack and send a massive volume of requests to the target.
Step 2: Types
of attack
DDoS attacks can take various forms, depending on the attacker’s objectives and the vulnerabilities of the target system. Some common methods include:
- Volumetric attacks: These aim to exhaust the target network’s bandwidth by bombarding it with a flood of data packets.
- Protocol attacks: This type of attack focuses on exploiting vulnerabilities in the protocol stack to overload the server and disrupt the service.
- Application-layer attacks: These specifically target web applications and attempt to overload the server by exploiting specific functionalities or vulnerabilities in the application logic.
Step 3: Execution
Once the botnet has been set up and the type of attack selected, the attacker launches the DDoS attack by instructing the bots to send requests to the target simultaneously. These requests can be as simple as repeatedly requesting a web server’s homepage or as complex as executing database queries. The aim is to flood the server with so many requests that it can no longer process legitimate requests.
Step 4: The Consequences
The immediate consequence of a successful DDoS attack is that legitimate users are unable to access the services or information hosted on the target server. This can lead to significant financial losses, damage to reputation and, in some cases, legal consequences.
DDoS attacks highlight the importance of robust cyber security measures. Organisations must invest in preventative security solutions, carry out regular security audits and develop contingency plans to protect themselves against such attacks and ensure the continuity of their operations.
Adapting security strategies
To keep pace with evolving threat patterns, organisations must continuously adapt their cybersecurity strategies. This involves implementing advanced detection systems capable of identifying even minor anomalies in network traffic. Furthermore, the use of machine learning and AI-based systems is crucial for recognising patterns in traffic anomalies and neutralising potential threats in real time.
Another important aspect is training staff to keep them informed about the latest cyber security threats and best practices. Given that many attacks are made possible by human error, the awareness and vigilance of every individual are an indispensable part of a company’s cyber security strategy.
Conclusion
The evolution of cyber threats, particularly DDoS attacks, shows that cyber security can never be static. Attackers are constantly developing new methods to circumvent security measures, and it is up to us to adapt our defence strategies accordingly. By investing in advanced detection technologies, providing ongoing staff training and developing proactive security measures, we can